As digital assets become increasingly mainstream, one question keeps compliance teams up at night: how do you treat transfers between hosted vs unhosted wallets when regulatory guidance remains murky? Both wallet types are legitimate — yet they carry very different risk profiles and visibility. In the world of AML/CFT, the shift from traditional bank-account custody to self-custody raises a simple but critical question: who really has the keys — and the data? This guide compares hosted vs unhosted wallets from an AML perspective.
Understanding Hosted vs Unhosted Wallets
A hosted wallet is operated by a regulated third-party — typically a crypto exchange, custody provider or VASP — which holds the private keys on behalf of the user, applies KYC/AML, and acts analogously to a bank account.
By contrast, an unhosted wallet (also called self-custody or non-custodial) places full control of the keys in the hands of the user.
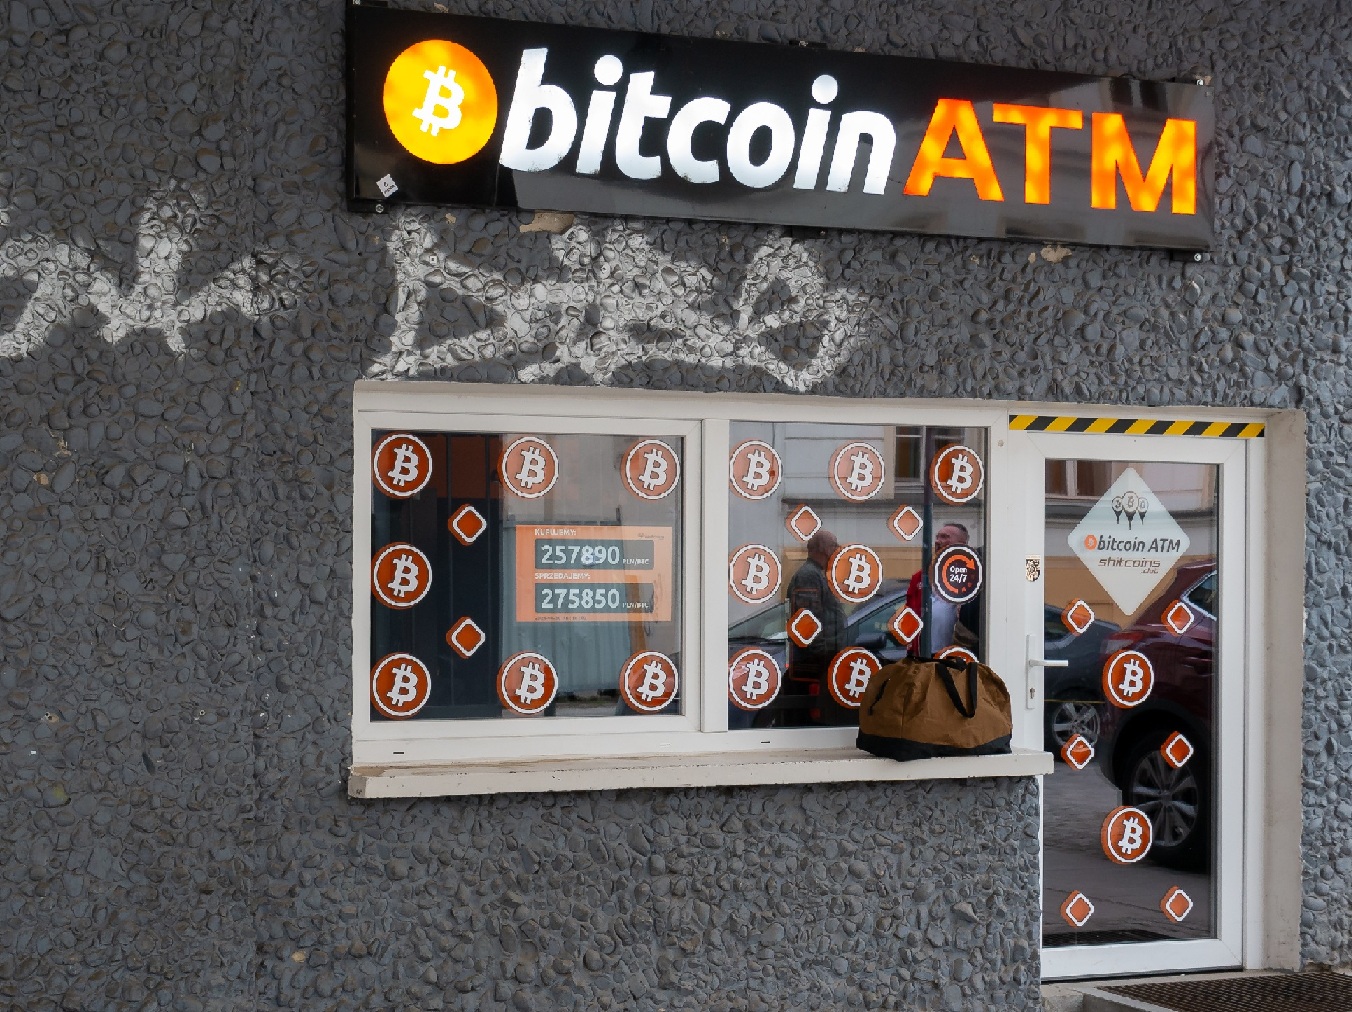
The difference between hosted vs unhosted wallets isn’t just technical — it fundamentally alters how traceability, identity and risk are handled by institutions that engage with crypto. Crypto ATMs are a practical example: cash goes in and crypto goes out to a wallet the operator may not host (see why crypto ATMs raise compliance concerns).

Hosted vs unhosted wallets at a glance
| Hosted wallet | Unhosted wallet | |
|---|---|---|
| Who holds the private keys | A third party (exchange, custodian, VASP) | The user |
| KYC/AML applied to the wallet holder | Yes, by the provider | Not by default |
| Visibility for the institution | The provider holds customer and transaction data | Only public blockchain data |
| Typical controls | Standard CDD and transaction monitoring | Ownership assessment where required, blockchain analytics, risk-based limits |
Regulatory Landscape and What It Means for Compliance
Globally the obligation to monitor and mitigate risk remains with the regulated entity — even when the counterparty uses an unhosted wallet. For example, the Financial Action Task Force has repeatedly flagged peer-to-peer transfers between unhosted wallets as a gap, because no regulated intermediary applies customer due diligence to them.
In the EU, the Transfer of Funds Regulation (Regulation (EU) 2023/1113, applicable since 30 December 2024) requires crypto-asset service providers to collect originator and beneficiary information for transfers to or from self-hosted addresses. Above EUR 1 000, the provider must also take adequate measures to assess whether the address is owned or controlled by its client (the originator when sending, the beneficiary when receiving).
While many jurisdictions (especially the U.S.) still lack clear rules for unhosted-wallet interactions, institutions can no longer wait for perfection. The regulatory expectation is already shifting. In March 2026 the FATF published a targeted report on stablecoins and unhosted wallets, which describes peer-to-peer transfers as taking place without a regulated intermediary.
Practical Risk-Management Approaches for Institutions
Given the ambiguity, institutions must adopt a risk-based approach rather than a one-size-fits-all ban on unhosted wallet use. A key tactic is to deploy blockchain analytics to ask not whose wallet is this? but rather, what risk does this wallet carry? According to the Elliptic article, “The question isn’t whose wallet it is — it’s what risks it carries.” Using blockchain analytics, compliance teams can screen wallet histories for links to sanctions, darknet markets or mixer services. Myself I did one Elliptic certification recently, and let me tell you that they can track hundreds hops away, and calculate risk of a wallet based on that.
Another effective strategy: apply tiered transaction thresholds (e.g., lower controls below €10 000, enhanced diligence above €50 000) and maintain whitelists and blacklists of self-custody addresses based on risk exposure. These tactics strike a balance between enabling access and safeguarding against illicit flows.
“The question isn’t whose wallet it is — it’s what risks it carries.”
The Outlook for AML Compliance
As the crypto-asset ecosystem matures, the real distinction will no longer be simply hosted vs unhosted — it will be visibility and behavior. Institutions must demonstrate that they can trace, assess and document flows even when a counterparty controls their own wallet. Blockchain transparency offers a new compliance frontier where on-chain analytics substitute for missing customer verification. In short: it’s not just about control of the private key — it’s about control of risk.
The sooner compliance teams build defensible, auditable processes for unhosted-wallet interactions, the better positioned they will be as rules develop.
The same visibility problem appears in correspondent banking; see payable-through accounts and the invisible customer problem.
Thanks to Elliptic for their detailed industry analysis on hosted vs unhosted wallets, which continues to shape the conversation around risk-based compliance in the digital-asset ecosystem.
Leave a Reply